Secure Enterprise Knowledge Search

Plugging your internal documents into a public AI search tool is a fast way to end up with a compliance problem — if the search doesn't respect who's allowed to see what, it becomes a shortcut around every access control you've set up.

We build search that's permission-aware from the ground up, so a result is never shown to someone who couldn't already open the source document — and every query is logged for audit.

Whether you're in a regulated industry with strict data residency requirements or just don't want internal search doubling as a data leak, we architect around your actual security posture.

What We Build Into Your Search

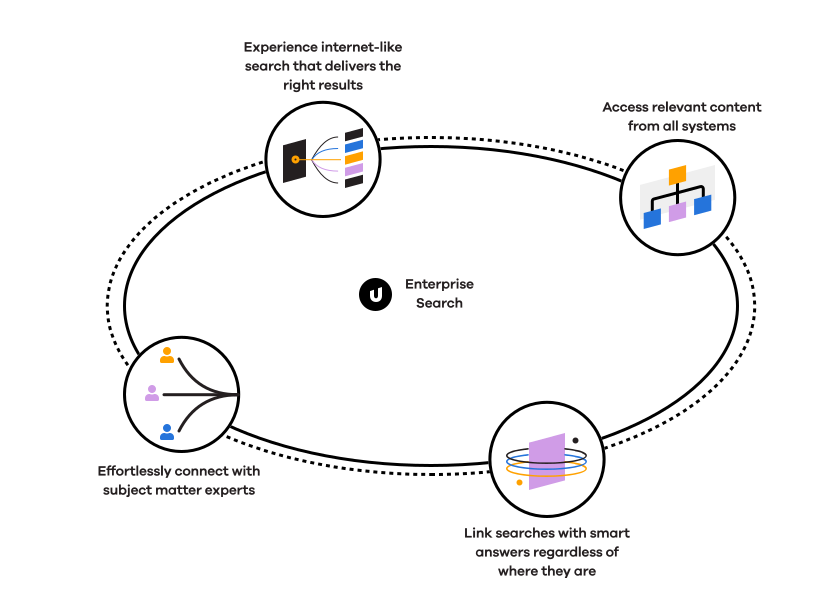
1. Permission-Aware Results, Always: Search results are filtered against your existing access control system in real time, so a result a user can't already open never appears.
Secure Knowledge Search

2. Encryption at Every Layer: Data is encrypted in transit and at rest, including the vector embeddings themselves, not just the original documents.

3. Full Query Audit Logging: Every search and every result shown is logged, so you can answer "who searched for what and when" if compliance ever asks.

4. On-Prem or Private Cloud Deployment: For regulated industries, the entire search stack — indexing, embeddings, and the model — can run inside your own environment instead of a third-party API.

5. No Data Leaves Without a Reason: We architect the pipeline so sensitive content isn't sent to external services it doesn't need to touch, closing off the most common accidental-leak path.

Why Choose Akantik for Secure Knowledge Search?

Most AI search tools are built for convenience first and permissions as an afterthought. We build it the other way around — security is the starting requirement, not a retrofit.

Security Reviewed Before Launch, Not After: We work with your security and compliance team during design, not after a review flags a problem post-launch.

Experience With Regulated Environments: We've built search for teams under HIPAA, SOC 2, and similar constraints, so the requirements aren't a surprise mid-project.

Deployment Options That Match Your Risk Tolerance: From fully managed to fully on-prem, we architect around what your data governance actually requires.

Need internal search that won't become a compliance liability? Let's design it around your actual access controls.

Secure Knowledge Search

Secure Knowledge Search - Frequently Asked Questions

Common questions about building permission-aware, secure AI search for internal data.

What makes search 'secure' compared to a standard AI search tool?

Secure knowledge search:

  • Filters every result against your existing access control system in real time
  • Encrypts data at every layer, including embeddings
  • Logs every query for audit purposes
  • Can be deployed entirely within your own environment
How does the search know what a user is allowed to see?

We integrate with your existing identity and permission system — such as Active Directory, SharePoint permissions, or a custom access control model — so search results are filtered the same way document access already is.

Can this be deployed fully on-prem or in a private cloud?

Yes, for organizations with strict data residency or compliance requirements, we can deploy the entire stack — indexing, embeddings, and the language model — inside your own infrastructure instead of relying on a third-party API.

Is this suitable for regulated industries like healthcare or finance?

Yes, we've built secure search for teams operating under HIPAA, SOC 2, and similar regulatory frameworks. Audit logging, encryption, and deployment options are designed to align with those requirements from the start.

Does secure search sacrifice speed or relevance for safety?

No, permission filtering happens efficiently alongside retrieval, and hybrid search techniques keep relevance high.

The security layer adds a real but small amount of latency in exchange for eliminating a serious data exposure risk.

Hire Us